It was a week that underscored how deeply interconnected global security, institutional trust, and emerging technology have become — and how professionals in Hyderabad's booming IT and startup ecosystem are not insulated from these developments, no matter how far away they unfold.
Espionage Inside OpenAI: A Warning for the AI Industry
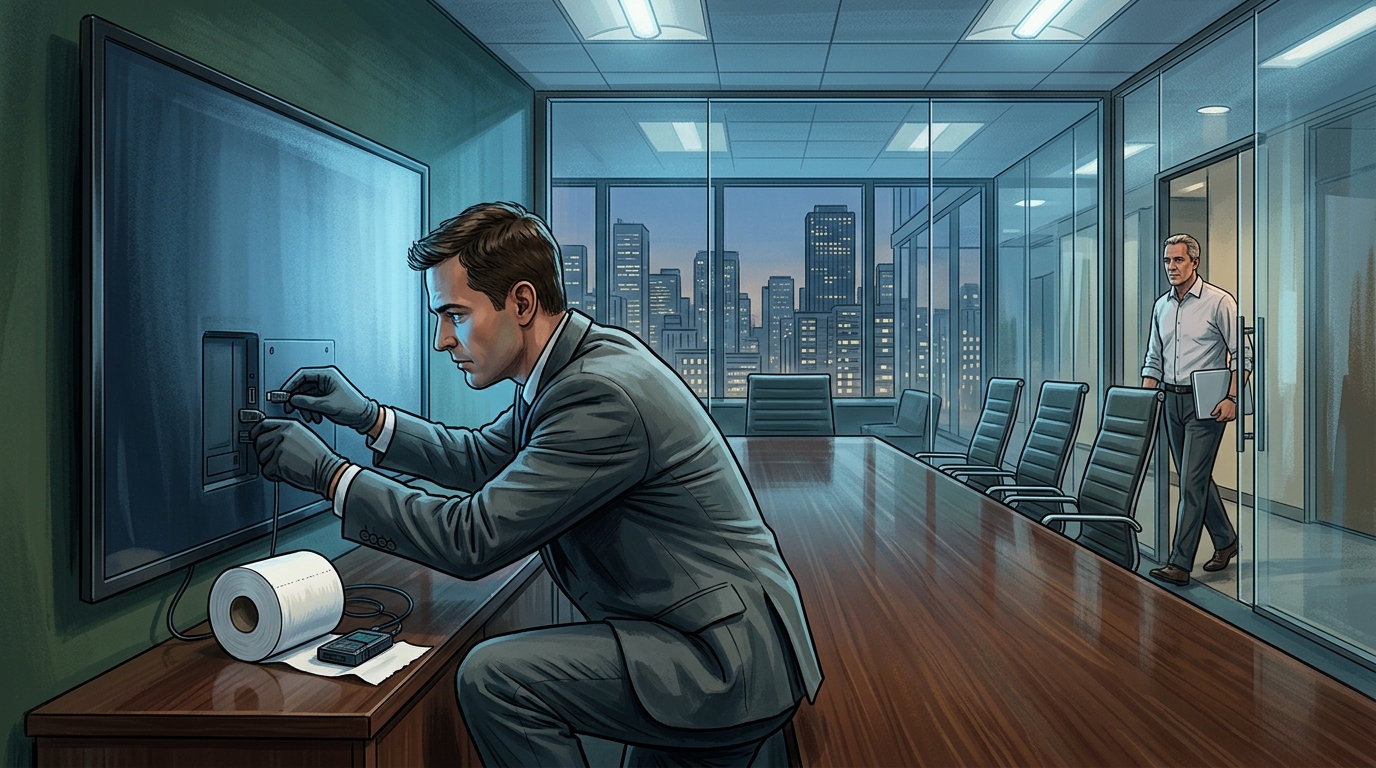
Perhaps the most striking story for the global tech community this week came out of San Francisco, where a Saudi national was charged with planting a sophisticated recording device inside OpenAI's executive conference room. The device — concealed in toilet paper and inserted into a USB port on the back of a television — was allegedly designed to capture conversations at the highest levels of one of the world's most consequential AI companies.
This is not merely a corporate espionage curiosity. OpenAI sits at the centre of global AI development, shaping tools that Hyderabad's software engineers, product managers, and AI startups either build upon or compete with. The incident raises urgent questions about physical and digital security culture within the AI industry — an industry that often prioritises speed of deployment over institutional safeguards. For Indian IT services firms and AI-focused startups increasingly partnering with or licensing from global AI platforms, this is a reminder that the infrastructure of trust underpinning these relationships is fragile and actively targeted by state and non-state actors.
The case also invites a broader conversation about whose interests are being served by rapid, opaque AI development, and whether companies like OpenAI are investing sufficiently in the kind of security and governance frameworks that their enormous influence demands.
MI5's Stark Warning: AI as a National Security Threat Vector
Compounding concerns about AI governance, MI5 Director General Sir Ken McCallum issued a significant public warning this week, stating that threats to the United Kingdom from Russia, Iran, and artificial intelligence have now reached roughly equal scale with traditional terrorism. This is an extraordinary framing — placing a technology category alongside hostile nation-states as a peer-level threat.
McCallum's remarks signal something the global tech industry has been slow to internalise: that AI is no longer just a productivity tool or a competitive advantage. It is increasingly a vector for misinformation, cyberattack orchestration, and influence operations. For Hyderabad professionals working in cybersecurity, cloud infrastructure, or enterprise software — particularly those serving UK or European clients — this kind of high-level intelligence assessment shapes regulatory priorities and procurement decisions in ways that will eventually land in contract clauses and compliance requirements.
A worker-friendly reading of this moment would argue that rank-and-file software engineers and data scientists deserve clearer institutional guidance — from both employers and governments — about the ethical and security dimensions of the systems they are building. The burden of responsible AI cannot rest solely on individual conscience when the stakes have become, by MI5's own reckoning, matters of national security.
The Pope's Health and the Stability of Global Institutions
The Vatican's announcement that Pope Leo underwent successful surgery to remove a lobe of his right lung following a lung cancer diagnosis is, on its surface, a story about one man's health. But the papacy remains one of the world's most influential moral and diplomatic institutions, with significant bearing on global policy conversations around poverty, climate, and labour rights — issues that intersect meaningfully with the concerns of progressive professionals and civil society globally.
The successful surgery is reassuring, and the Vatican's transparency in communicating the diagnosis is worth noting as a standard of institutional accountability that many more powerful organisations fail to meet.
What This Means for You
- AI security is now a board-level concern: If your startup or employer works with AI platforms or stores sensitive data in AI-integrated environments, the OpenAI breach attempt is a prompt to audit physical and digital security practices — not just software vulnerabilities.
- Compliance landscapes are shifting: MI5's framing of AI as a national security threat will accelerate regulatory action in the UK and EU. IT professionals and founders with Western clients should watch for new compliance requirements around AI use disclosure and data handling.
- Geopolitical risk is AI risk: State-sponsored espionage targeting AI companies signals that the technology your team builds or depends on is geopolitically contested territory. Diversifying toolchains and understanding the provenance of AI infrastructure is increasingly prudent risk management, not paranoia.
- Institutional transparency matters: Whether it is the Vatican, MI5, or a tech giant, the week demonstrated that how institutions communicate risk and crisis shapes public trust. For founders and leaders, there is a lesson here about the long-term value of honest, timely communication with stakeholders.
The world's most consequential institutions — intelligence agencies, the Catholic Church, and AI laboratories — all surfaced in the same news cycle this week, each grappling with threats they are only beginning to understand. For Hyderabad's professionals, the message is clear: global turbulence is not background noise. It is the operating environment.